The loudest event in a threat report is not necessarily the one that should consume most of a company's security budget. ENISA recorded denial-of-service activity in just over half of the incidents in its 2026 Threat Landscape, yet it describes financially motivated activity, especially ransomware, as the most disruptive threat in the short term. The useful lesson for a growing organisation is therefore not "buy more DDoS protection" or "train everyone about phishing" in isolation. It is to defend the access chain that joins a lure, a stolen session, an exposed service or an exploited vulnerability to data theft and extortion.
That chain also explains one of the report's less obvious findings: cybercriminal, hacktivist and state-linked operators increasingly reuse similar access routes, tools and trusted digital environments even when their goals differ. Controls organised around attacker labels will age badly. Controls that reduce unauthorised access, contain compromised identities and make recovery credible will travel much further.
What ENISA measured, and what it did not
The latest report available on 30 September 2026 is the ENISA Threat Landscape 2026, published on 22 September 2026. Its title and publication date should not be mistaken for its observation window. ENISA analysed 8,257 incidents recorded from 1 January to 31 December 2025. The move to a calendar-year window creates a six-month overlap with the preceding ETL 2025 report.
The dataset was assembled mainly from open sources, with anonymised information from EU Member States and members of the ENISA Cyber Partnership Programme. ENISA also widened its tracking of cybercrime activity, including data breaches and fraud. It says this affected the numbers but did not materially change the rankings and trends.
The report groups its main analysis around cybercrime, state-nexus activity, foreign information manipulation and interference (FIMI), hacktivism and vulnerabilities. These are analytical categories, not five mutually exclusive queues for defenders. ENISA explicitly notes overlaps among fraud, breach, scam and ransomware records, and observes that the boundaries between actor categories are blurring.
A compact reading of the dataset is useful:
| Measure | ENISA finding | Operational reading |
|---|---|---|
| DDoS share of recorded incidents | 51.3% | High-volume activity, often with limited or temporary impact |
| Unauthorised access | 39.5% | The incident class that connects exposure and identity failure to later harm |
| Ideology-driven incidents | 57.3% | Mostly shaped by hacktivist DDoS claims and geopolitical events |
| Financially motivated incidents | 29.2% | Lower volume than ideology-driven activity, but greater short-term impact |
| Cyberespionage | 6.3% | Lower visibility and often delayed reporting; a strategic, longer-term threat |
| Essential and important entities | 72.9% of recorded incidents | The dataset is strongly relevant to NIS2 sectors, not a census of every EU business |
These percentages describe ENISA's collected sample. They are not annual probabilities that a particular company will be attacked.
Volume and impact point in different directions
DDoS dominated the count, and public administration was the most targeted sector at 31.8%. That sector's profile was heavily affected by ideology-driven DDoS: 81.8% of its recorded incidents. Public-facing sites and portals were repeatedly targeted around elections, arrests, political statements and geopolitical developments. Many claims produced limited or temporary disruption.
Ransomware tells a different story. ENISA calls it the most impactful incident type in the short term. Ransomware deployment represented 47.3% of financially motivated activity; manufacturing accounted for 25.2% of ransomware claims and business services 18.7%. Operators combined encryption, theft and public extortion rather than relying on encryption alone.
This distinction matters for a smaller security team. A weekly chart of events rewards what is easy to count. Risk decisions need a second axis: plausible business impact. A short website outage, theft of an administrator session and encryption of a production environment cannot be ranked by frequency alone.
The access chain is the practical threat model
ENISA could identify an intrusion vector for only 5.2% of unauthorised-access incidents. Within that limited subset, exploitation of vulnerabilities accounted for 60.4%, while misconfiguration and accidental exposure accounted for 20.7%. The small denominator is essential context; 60.4% must not be presented as the share of all incidents caused by vulnerabilities.
Social engineering supplies another part of the chain. Among identified social-engineering techniques, phishing represented 77.8% and malicious spam 13%. ENISA also observed more ClickFix activity, phishing kits and phishing-as-a-service. Elsewhere in the report, infostealers are described as a source of credentials, browser data, MFA tokens and session cookies used for account takeover, access brokerage, fraud and ransomware.
Cloud and SaaS compromise makes the boundary between "identity" and "infrastructure" increasingly artificial. The report describes operators using voice phishing, credential harvesting, MFA abuse and stolen OAuth tokens to enter enterprise cloud environments, then reaching connected services and extracting data. It also records continued targeting of software suppliers, service providers, cloud environments, repositories, browser extensions and packages.
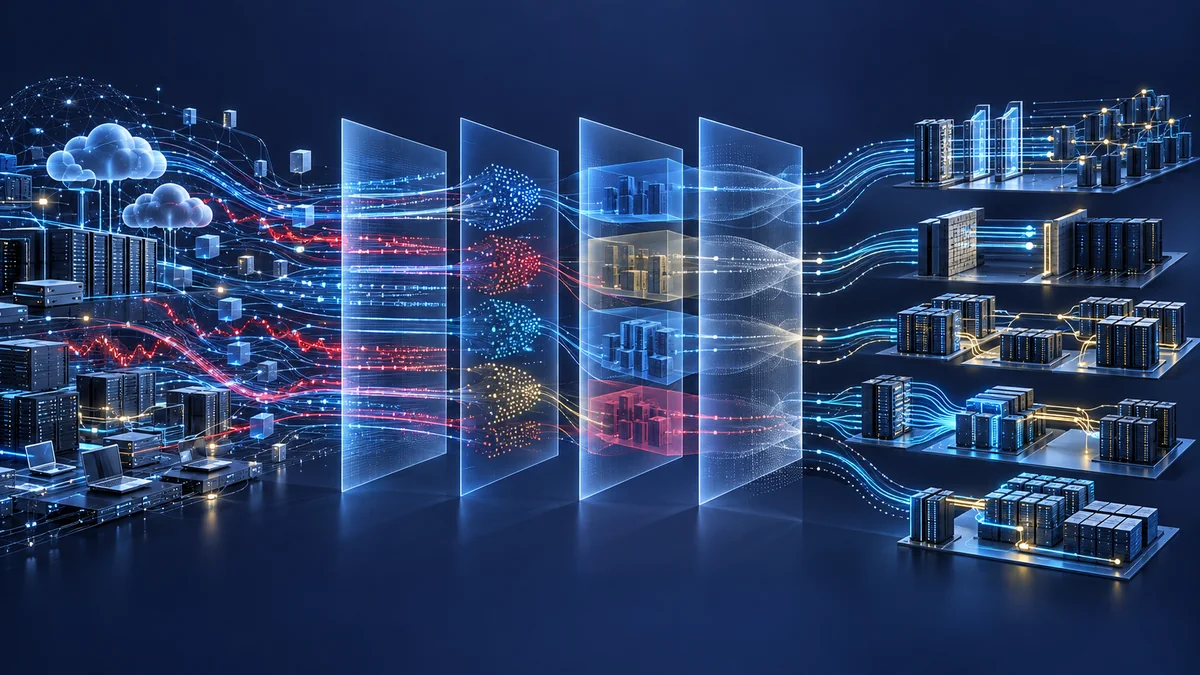
The pattern is not a single top threat. It is convergence:
- a person, edge service, supplier or software component provides initial access;
- an identity, token or trusted workflow turns that foothold into usable privilege;
- connected SaaS, cloud and third-party relationships expand the reachable environment;
- data theft, disruption, fraud or ransomware produces the business impact.
Different operators can buy, borrow or reuse the same pieces. That is why the first defensive question should be "which paths give an attacker durable access?", not "which named group are we most likely to face?"
Sector and geography: useful calibration, poor prophecy
Across all recorded incidents, ENISA's five most targeted sectors were public administration (31.8%), business services (8.5%), transport (8%), manufacturing (6.9%) and finance/banking (5.6%). The picture changes when the lens narrows to cybercrime: manufacturing led with 14.4%, followed by business services at 13.5%, finance/banking at 9.2% and public administration at 8.7%.
The EU geographic pattern also depends on the activity being measured. Germany accounted for 18.1% of identified financially motivated events, Spain 17.7%, France 17.6%, Italy 12.6% and the Netherlands 4.6%. For ransomware claims specifically, Germany led at 26.5%, followed by France at 14.7%, Italy at 13.6%, Spain at 12.2% and the Netherlands at 4.7%. Hacktivist claims followed another distribution and shifted from quarter to quarter with political events.
For organisations in Spain, the 17.7% share is a reason to test assumptions, not a forecast. It may reflect economic size, reporting visibility, collection choices or operator attention. A Spanish manufacturer with remote maintenance and weak recovery should read the ransomware and exploitation findings more closely than the all-incident sector ranking.
Five priorities for a growing organisation
1. Reconcile external exposure with exploitable paths
Start with what the internet can reach, then connect each service to an owner, business purpose, authentication method, support status and remediation deadline. An asset list without external validation misses forgotten endpoints; a scanner without ownership produces recurring alerts. Our guide to reconciling internet-exposed assets with the inventory sets out that operating loop.
Prioritise known exploited or readily exploitable weaknesses on public-facing systems, remote access, identity infrastructure and management planes. A severity score alone does not express reachability or blast radius. A vulnerability-management programme should combine exploit evidence, exposure, privilege and business criticality.
2. Treat sessions and tokens as credentials
Phishing-resistant MFA is valuable, but the report shows why MFA enrolment cannot be the finish line. Review legacy authentication, device-code flows, OAuth consent, service accounts, API keys, browser sessions and help-desk recovery. Restrict administrative access to managed devices, shorten risky session lifetimes and alert on impossible or unusual token use. Make privileged access revocable quickly.
3. Put dependencies inside the incident boundary
List the providers that can administer systems, hold sensitive data, issue identities, deploy code or interrupt operations. For each one, document the technical connection, responsible owner, notification route, evidence you can obtain during an incident and a fallback. ENISA's examples show that a provider compromise can turn one intrusion into many downstream incidents.
4. Build detection around the chain, then rehearse recovery
Log the events needed to connect an initial access attempt to later actions: identity-provider sign-ins, MFA and token changes, endpoint execution, administrative actions, SaaS audit events, egress and backup operations. Collecting everything indefinitely is not the goal. Security logging for SMBs explains how to start with questions the team can actually investigate.
Then test whether backups are isolated, restorable and sufficient to run the business. Include stolen data and public extortion in the exercise. Restoring servers does not answer legal, customer or fraud decisions after exfiltration.
5. Measure paths closed, not alerts accumulated
Useful measures include the number of public services without an owner, exploitable external findings past deadline, privileged accounts without phishing-resistant authentication, third parties with unreviewed access, and critical services that failed a restore test. These indicators show whether attack paths are shrinking. Raw alert volume does not.
Where the EU evidence travels, and where it stops
The report's evidence base concerns EU Member States and EU-based organisations. Its sector labels, NIS2 framing and geopolitical patterns are European. It should not be converted into a global or Latin American prevalence study.
The operational chain does travel. Credential theft, exposed services, vulnerable edge systems, cloud tokens, supplier access and extortion are not EU-only mechanisms. An organisation in Latin America can use the report to challenge controls and scenario plans, but should calibrate actor activity, sector concentration, local fraud patterns and incident frequency with national CSIRT reporting and its own telemetry. The EU percentages should not be copied into a LATAM risk register as local probabilities.
Read the findings with their limits intact
ENISA says the open-source and voluntarily shared information does not provide a complete picture. Vague geographic or sector reporting affects classification; one organisation may span several sectors; incidents may be reported late or not confirmed. Visible events such as DDoS and ransomware claims appear quickly, whereas cyberespionage reporting can lag by six months to more than four years. Increased coverage can also reflect public interest rather than a real increase in activity.
The methodology adds useful controls: daily collection, EU-relevance scoring, source reliability and credibility ratings, semi-manual correlation, expert analysis and internal or stakeholder review. AI-supported tools may assist monitoring, collection and limited editing, but ENISA says analysts, not AI, identify trends and make assessments.
There is no public incident-level dataset download linked from the report page. Readers can inspect the methodology, figures and source notes, but cannot independently reproduce every percentage from the 8,257 underlying records. ENISA also changed the reporting window and expanded cybercrime tracking, so direct year-on-year comparisons need care.
The decision to take from the report
ENISA's numbers do not justify chasing five separate threat lists. They justify reducing the routes that many operators share. Find exposed and exploitable services. Make identity and token abuse harder. Limit what a compromised supplier can reach. Preserve the evidence needed to investigate. Prove that critical operations can recover.
For a small or growing organisation, that is a manageable programme because it follows attack paths rather than headlines. If you need help identifying the paths that matter most, Enclave Guard's Cyber Threat Intelligence and Continuous Exposure Management service can connect external exposure and threat context to owned remediation decisions.